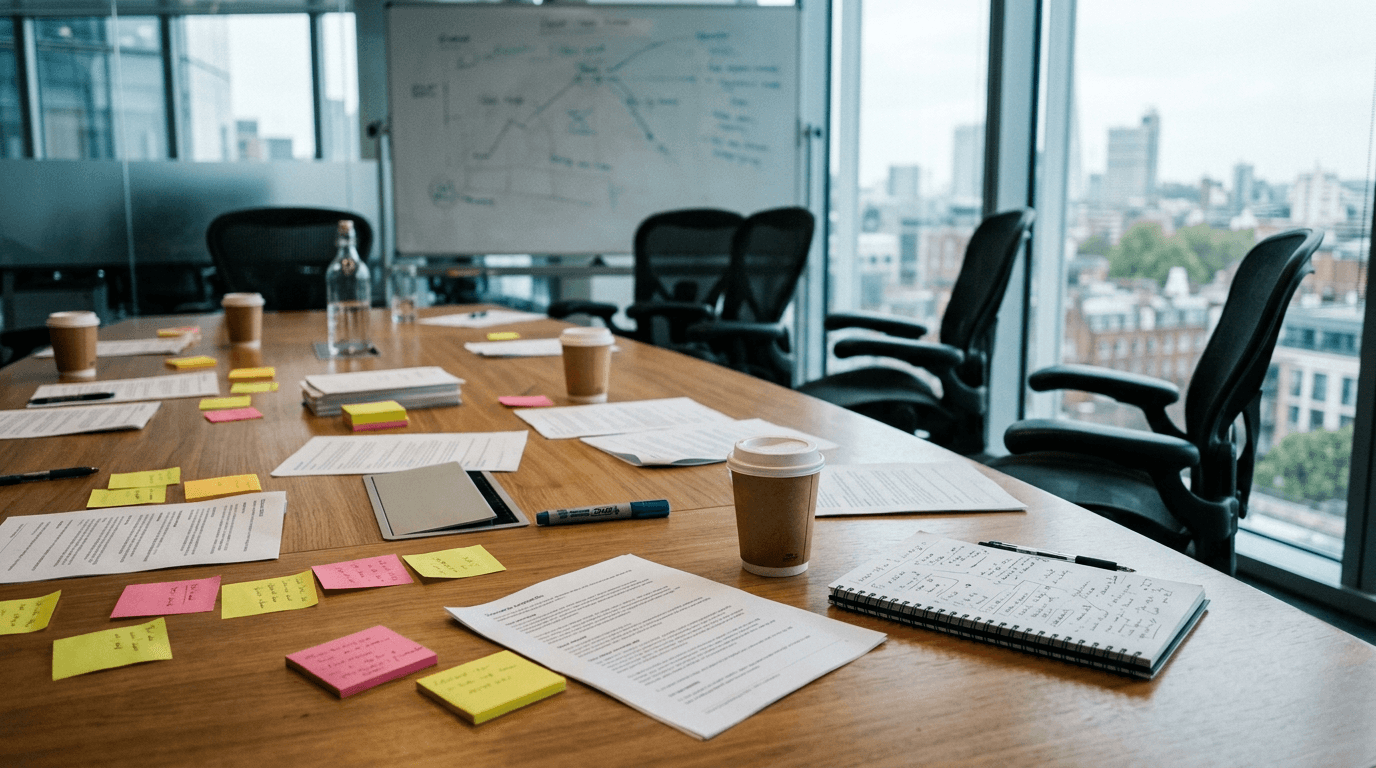
A ransomware tabletop exercise is a two-hour meeting where the people who would respond to an attack talk through a realistic ransomware scenario, step by step, to find out what your incident response plan actually does. Nothing gets unplugged: a facilitator reads out what is happening and asks who does what next. It costs a conference room and two hours, and it's the cheapest way to discover that the person who holds your backup credentials left in March.
Here are the questions owners ask us before they run their first one, followed by a ransomware scenario you can run yourself.
Tabletop exercise questions owners ask
What is a cybersecurity tabletop exercise?
A facilitated discussion, not a technical test. Somebody reads out a scenario, say a ransomware note on the file server, and the people who'd have to respond talk through what they'd each do, step by step. Nothing gets unplugged and no systems are touched. The output is a list of things that don't work. NIST's exercise guide, SP 800-84, describes tabletops the same way: discussion-based only, with a facilitator presenting a scenario and asking questions about roles, responsibilities, coordination and decision-making. An incident response tabletop exercise is simply one built to test your incident response plan.
How long should it take?
Two hours for a first one. Ninety minutes of scenario and half an hour of debrief is enough to expose the big gaps without losing the room. Longer sessions get diminishing returns fast, because the same three problems keep surfacing. Run a short one this quarter rather than scheduling a half-day you'll postpone twice.
Who needs to be in the room?
The owner or a decision-maker, whoever handles IT, whoever handles money, and whoever would talk to customers. That last one gets skipped constantly and it's the one that hurts: someone has to answer the phone while the servers are down. Keep it under eight people. Your IT provider should facilitate, not answer for you.
What scenario should we run first?
Ransomware. It's the one that puts every part of the business on the table at once: backups, insurance, payroll, customer notification, and whether you can operate at all on day two. CISA's tabletop exercise packages cover ransomware, phishing, insider threats and industrial control system compromise, with more than 100 packages available. The scenario further down this page is a shorter ransomware version sized for a small business.
Do we need a written incident response plan first?
No, and waiting for one is how this gets deferred forever. Running the exercise is often the fastest way to write the plan, because the gaps it exposes become the plan's contents. If you already have a documented incident response plan, bring it and test whether it survives contact with a real scenario.
How often should we run one?
Annually at minimum, and again after anything that changes who does what: a new IT provider, an acquisition, losing the person who knew where everything was. Rotate the scenario so you're not rehearsing the same answer. The second exercise is usually more useful than the first, because people stop performing and start arguing about specifics.
What does a tabletop exercise cost?
Less than most owners assume. CISA provides its exercise packages to stakeholders on request, so the real cost is mostly the time of the people in the room plus a facilitator if you use one. What moves a facilitator's quote is the number of participants and sessions, whether the scenario is built around your own systems and vendors, and how detailed the after-action report needs to be. Compare that to what a breach costs: IBM's Cost of a Data Breach Report 2026 puts the global average at USD 4.99 million, a record high.
Does cyber insurance or compliance require one?
Requirements vary by carrier and framework, so read your own policy rather than trusting a general answer. What's consistent is direction of travel: in the renewal applications we've reviewed over the past two years, carriers increasingly ask about response readiness, and NIST's current incident response guidance, SP 800-61 Revision 3 (April 2025) frames preparedness as ongoing risk management rather than a document you file.
What should come out of it?
A short written list, assigned to named people with dates. Not a report nobody reads. If the exercise surfaced that nobody's tested a restore in a year, that's one line with an owner and a deadline. CISA's packages include after-action report templates for exactly this. An exercise with no follow-up list was a conversation, not an exercise.
What usually goes wrong in the first one?
The same handful of things, almost every time. Nobody knows who declares an incident. The backup story is more confident than the last actual restore test justifies. The cyber insurance policy number lives in an inbox on an encrypted machine. And the contact list for staff is a spreadsheet on the file server that just got encrypted.
A ransomware tabletop exercise scenario you can run
This scenario is illustrative. Read each inject aloud, give the room ten to fifteen minutes on its questions, and have someone write down every "we don't know" as it happens.
- Monday, 7:40 a.m. Staff can't open shared files, and a ransom note sits on the file server. Who gets the first call? Who has the authority to declare an incident and take systems offline? Where is the plan, if the network is down?
- 8:30 a.m. IT confirms the file server and two laptops are encrypted. When was the last successful restore test? Could the attacker reach the backups from the infected network? Which systems come back first?
- 10:00 a.m. An email from the attackers claims they copied client files and will publish them. Who calls the cyber insurance carrier, and is the policy number reachable? Who calls counsel? What notification obligations might apply to the data involved?
- 1:00 p.m. A client calls to ask whether their data is safe, and a local reporter emails. Who speaks for the company, and what are they allowed to say today?
- Tuesday, 9:00 a.m. Payroll is due tomorrow and the accounting system is still down. Can the business run payroll and take orders manually? Who decides whether to engage with the ransom demand, and on what advice?
- Debrief. List each gap with an owner and a date, and decide which ones change the written plan.
Frequently asked questions
What's included when NetSys facilitates an exercise?
A scenario built around your systems, vendors and people, a facilitated two-hour session, and a written gap list with owners and dates afterward. For NetSys managed clients, tabletop exercises are part of our incident response planning and retainer service, which is included in the month-to-month managed agreement. Other businesses can engage the planning and exercises as a fixed-scope project.
How does getting started work?
A short scoping call first: who will be in the room, which systems and data matter most, and what plan, backups and cyber insurance you already have. We write the scenario from those answers, so the injects name your real systems instead of generic ones.
Who handles escalations if a real incident happens?
Your plan's incident lead decides, and the plan's contact sheet says who to call. For NetSys clients, monitoring and emergency service run 24/7, and the help desk is staffed seven days a week from 4 a.m. to 11 p.m. Eastern. An exercise is the right time to check that your staff know those numbers and that the authority to act is written down.
How is a tabletop different from a functional exercise?
A tabletop is discussion only. In NIST SP 800-84's terms, a functional exercise goes further and lets people validate their operational readiness by actually performing their duties in a simulated environment, for example restoring a server from backup against the clock. Most small businesses should run a tabletop first and a restore test second.
Sources and further reading
- CISA: Tabletop Exercise Packages (CTEPs): scenario library, discussion questions, and after-action report templates. Accessed October 2026.
- NIST SP 800-84: Guide to Test, Training, and Exercise Programs for IT Plans and Capabilities: the definitions of tabletop and functional exercises. Published September 2006.
- NIST SP 800-61 Rev. 3: Incident Response Recommendations and Considerations for Cybersecurity Risk Management: A CSF 2.0 Community Profile. Published April 2025.
- IBM: Cost of a Data Breach Report 2026: USD 4.99 million global average breach cost. Accessed October 2026.
If you've never run one, the first exercise is the one that finds the most. Book a call and we'll scope a facilitated tabletop against your environment, then hand you the gap list. It sits alongside our incident response and security assessment work.
By Joel Baum, who leads cybersecurity, compliance and security strategy at The NetSys Group. NetSys has delivered managed IT, cybersecurity, and cloud services since 1998, on site across New York City, Long Island, Westchester, the Hudson Valley, North Jersey and Fairfield County, Connecticut, and remote-first everywhere else.
Related reading
 FAQ
Lost or Stolen Work Laptop: 9 Questions Owners Ask
Read Article FAQ
Filing a Cyber Insurance Claim: 10 Questions Owners Ask
Read Article FAQ
IT Support for Manufacturers: 8 Questions Owners Ask
Read ArticleAlso on this topic: Incident Response Retainer Cost: Scope, Coverage and Agreement Questions · Incident Response vs Disaster Recovery vs Digital Forensics: Who Does What
Discuss ransomware protection & recovery for your business.
Tell us about your current systems, the result you need and your timeline. We will discuss the work, responsibilities and pricing before you decide on an engagement.